You built it with AI. We make it safe to launch.
Our Vibe Code Audit is an AI app security audit for apps built with Claude Code, Cursor, Lovable or Bolt. We test your app, close the gaps we find and set it up properly, so you can keep building safely. If it needs more than that, we’ll tell you straight.
Free first call · $6,000 + GST for internal tools · $10,000 + GST for customer-facing apps · Always-on Review from $2,500/month + GST

Built with any of these? This is for you.
- Claude Code
- Cursor
- Lovable
- Bolt
- Replit
- v0
- Base44
- Windsurf
- Codex
- Supabase
Engineering and software for some of Australia’s most trusted brands.
The systems behind brands you know.
Gelato Messina
Systems connected across close to 40 stores.
Production, warehouse and retail on one set of data, with app integrations for new customer experiences.
Tradies
51,000+ members on one app.
App development, with rostering, HR, payroll and POS connected so nothing is entered twice.
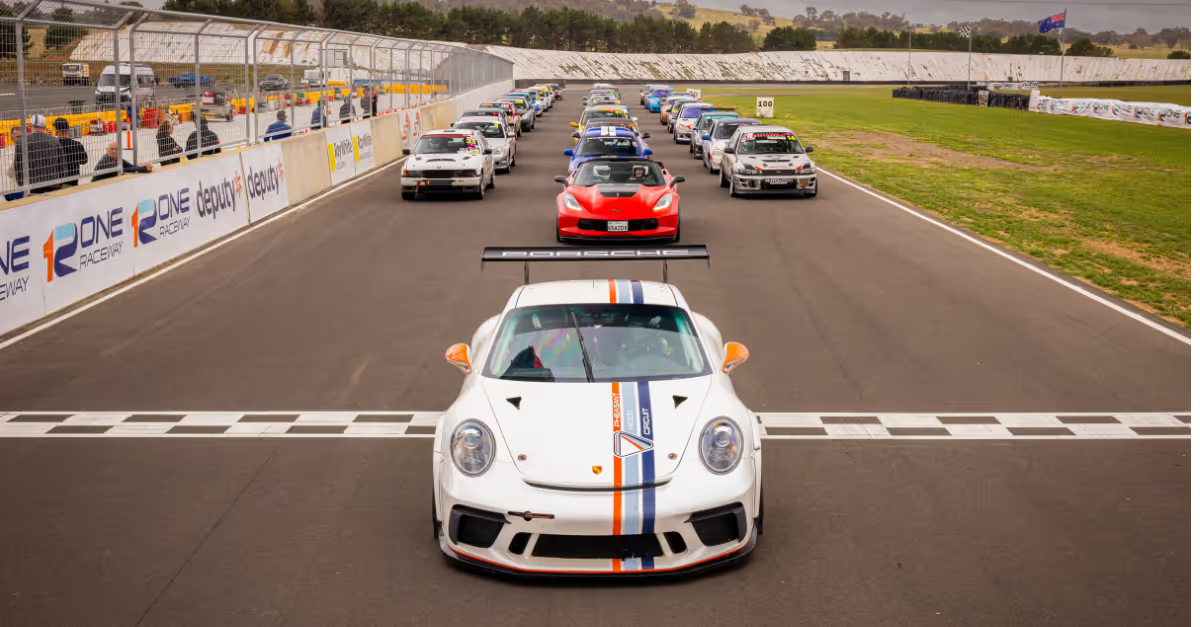
One Raceway
A motorsport venue’s tech, built from zero.
Over 10 km of fibre, 10+ platforms, and race-critical systems built for the track.
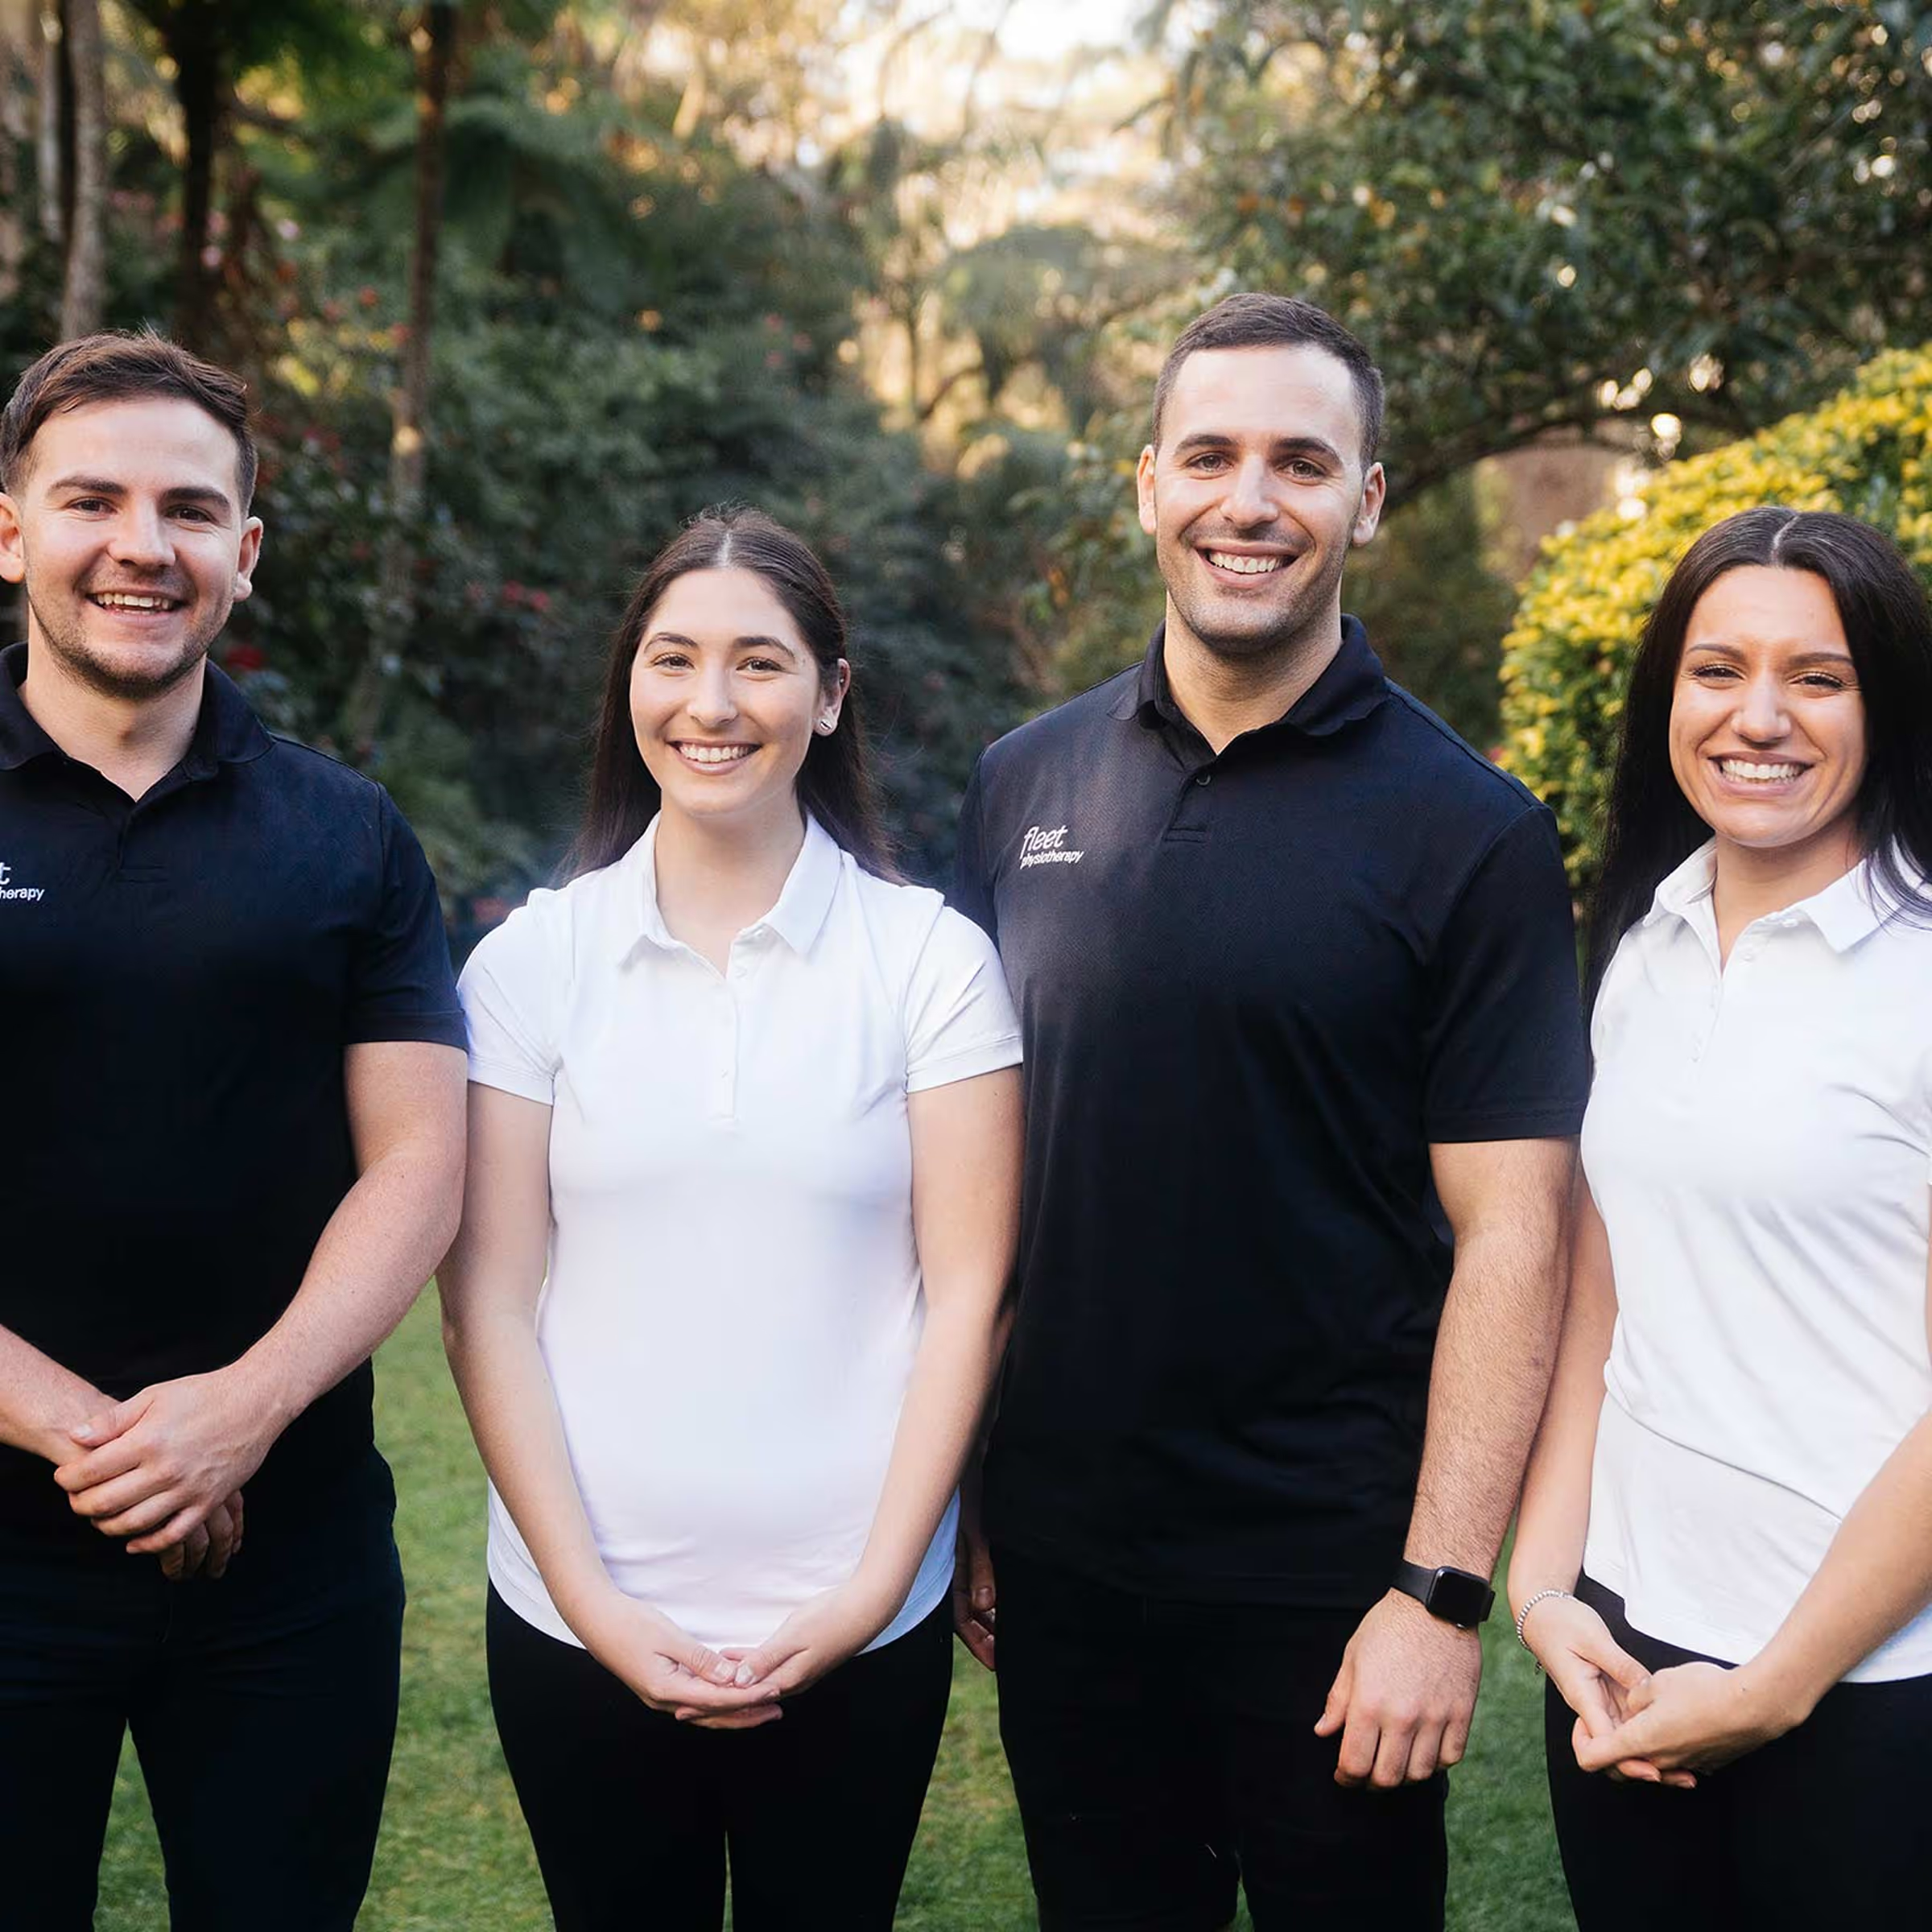
Fleet Healthcare
60% of simple queries answered automatically.
AI triage on referrals, and invoicing automated end to end.

What our clients say.
“With Jiffi, things move quickly, there’s no red tape, and they adapt to how we work. They’re flexible, responsive, and just great problem solvers.”
Michael Cross
Gelato Messina“After Jiffi stepped in, invoicing went from taking minutes to seconds, communications became structured and reliable, and nothing slipped through the cracks.”
Alex Hunt
Founder and Managing Director, Fleet Healthcare“Jake and Jiffi changed how I think about technology. We launched our own internal software, and now we’re helping our clients do the same.”
Adam Sullivan
Founder, Godspeed Digital
What we find in AI-built apps, and how we fix it.
The AI that built your app says it’s all hooked up. It’s not.
In Veracode’s 2026 GenAI Code Security Report, roughly 44% of AI code generation tasks introduced a security vulnerability.

Your old helper can still get in.
The mate or freelancer who set it up often still has admin access.
We find everyone who can get in, and remove anyone who shouldn’t.

Your customer data is one click away.
AI tools often leave data open to anyone with the link. No login needed.
We try to reach it logged out, then lock it down.

One client sees another’s records.
A parent sees another family’s details, or a customer opens someone else’s orders.
We log in as every type of user and fix what each one can see.

Your master key is sitting in public.
AI tools paste passwords and keys straight into the code.
We find them, move them somewhere safe and help you change them.

A Friday fix takes the whole team down.
There’s one version of the app, so every change goes straight to live.
We set up a test version, so changes get checked before your team sees them.

Every fix breaks something else.
There are no tests, so your customers find the bugs first.
We add automated checks that run before every release.
Everyone says they’ll make your app production-ready. Ask who audits them.
We’re ISO/IEC 27001:2022 certified and independently audited every year. Your code, hosting and IP stay in your name.

Software we’ve helped ship. Still running.
Built with AI tools, made safe to rely on, and kept online.
Trawly
LiveA morning briefing on what matters in your world, searched overnight. Built by David at Enviz.
Palate
LiveThe design taste layer for AI website builders, so what you build doesn’t look like everyone else’s. Built by Jake, and still being updated.
Clarity Club
LiveJiffi’s platform for operators: a health check that reads your real data, and the tools and sessions to build your own software.
Godspeed OS
Internal toolThe internal system an AI-enabled marketing agency runs on: content, clients and reporting. Built in a day, and shipping new features every week with the guardrails Jiffi helped set up.
Kinbox
PilotOne email address for every NDIS provider’s invoice. Each one is read and checked against the plan, then families pay everyone in one go.
Who is a vibe code audit for?
For businesses in care, disability, childcare, allied health, hospitality, trades and professional services, where a data mistake means a regulator, an insurer or an angry parent.
Founders about to let customers in
Where you are: It works on test data. Real customers log in soon.
What you get: Their data safe from day one.
Founders raising or selling
Where you are: Your lawyer, insurer, board or an investor wants to know who checked it.
What you get: An independent check from an ISO 27001 certified company.
Apps holding sensitive data
Where you are: Health details, payments, or records about kids and families.
What you get: Every user sees only their own records.
Agencies and freelancers
Where you are: You built it for a client with AI tools. Now it has to go live.
What you get: A check you can hand over with it.
Not sure if that’s you? Book a free 30-minute call and we’ll tell you straight.
How a vibe code audit runs.
Most audits take 4 to 5 days from kickoff. It all happens in your accounts, and nothing gets rebuilt.
After the audit
Always-on Review
From $2,500/month + GST. We review every risky change before it ships, because every new feature can open a gap.
Local engineers when you need them
New features, more security or more hands: our team in Sydney scales up or down with you.
Keep building it yourself
Your checks catch mistakes before your customers do, including the AI’s.
Who checks your app?
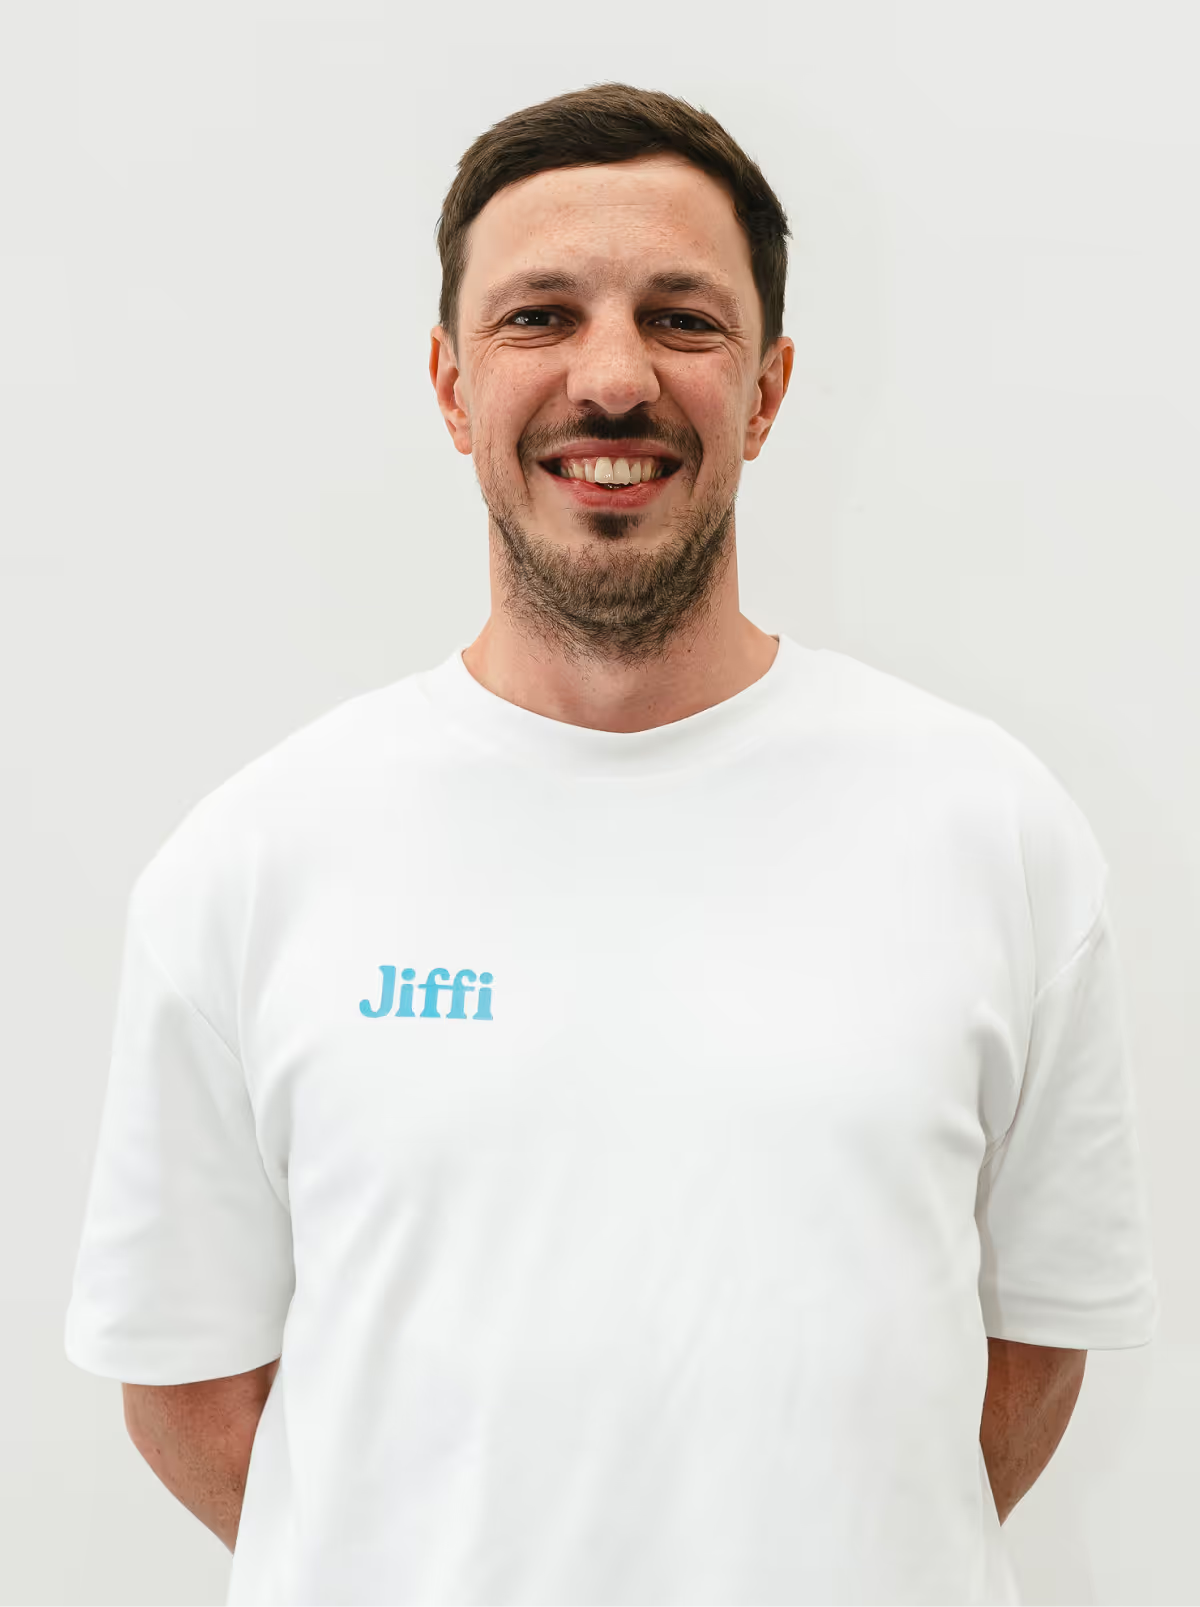
Joseph Pons
Co-founder, Head of Engineering and CISO
Joseph has more than a decade of experience in engineering, systems and SaaS delivery, including seven years in engineering leadership at Deputy. As Jiffi’s Chief Information Security Officer, he led the company to ISO/IEC 27001:2022 certification and runs the security program behind it.
“AI is brilliant at building things that work. It’s not great at telling you what it got wrong. That’s my job: I’ll test your app the way a stranger would, then help you fix it.”
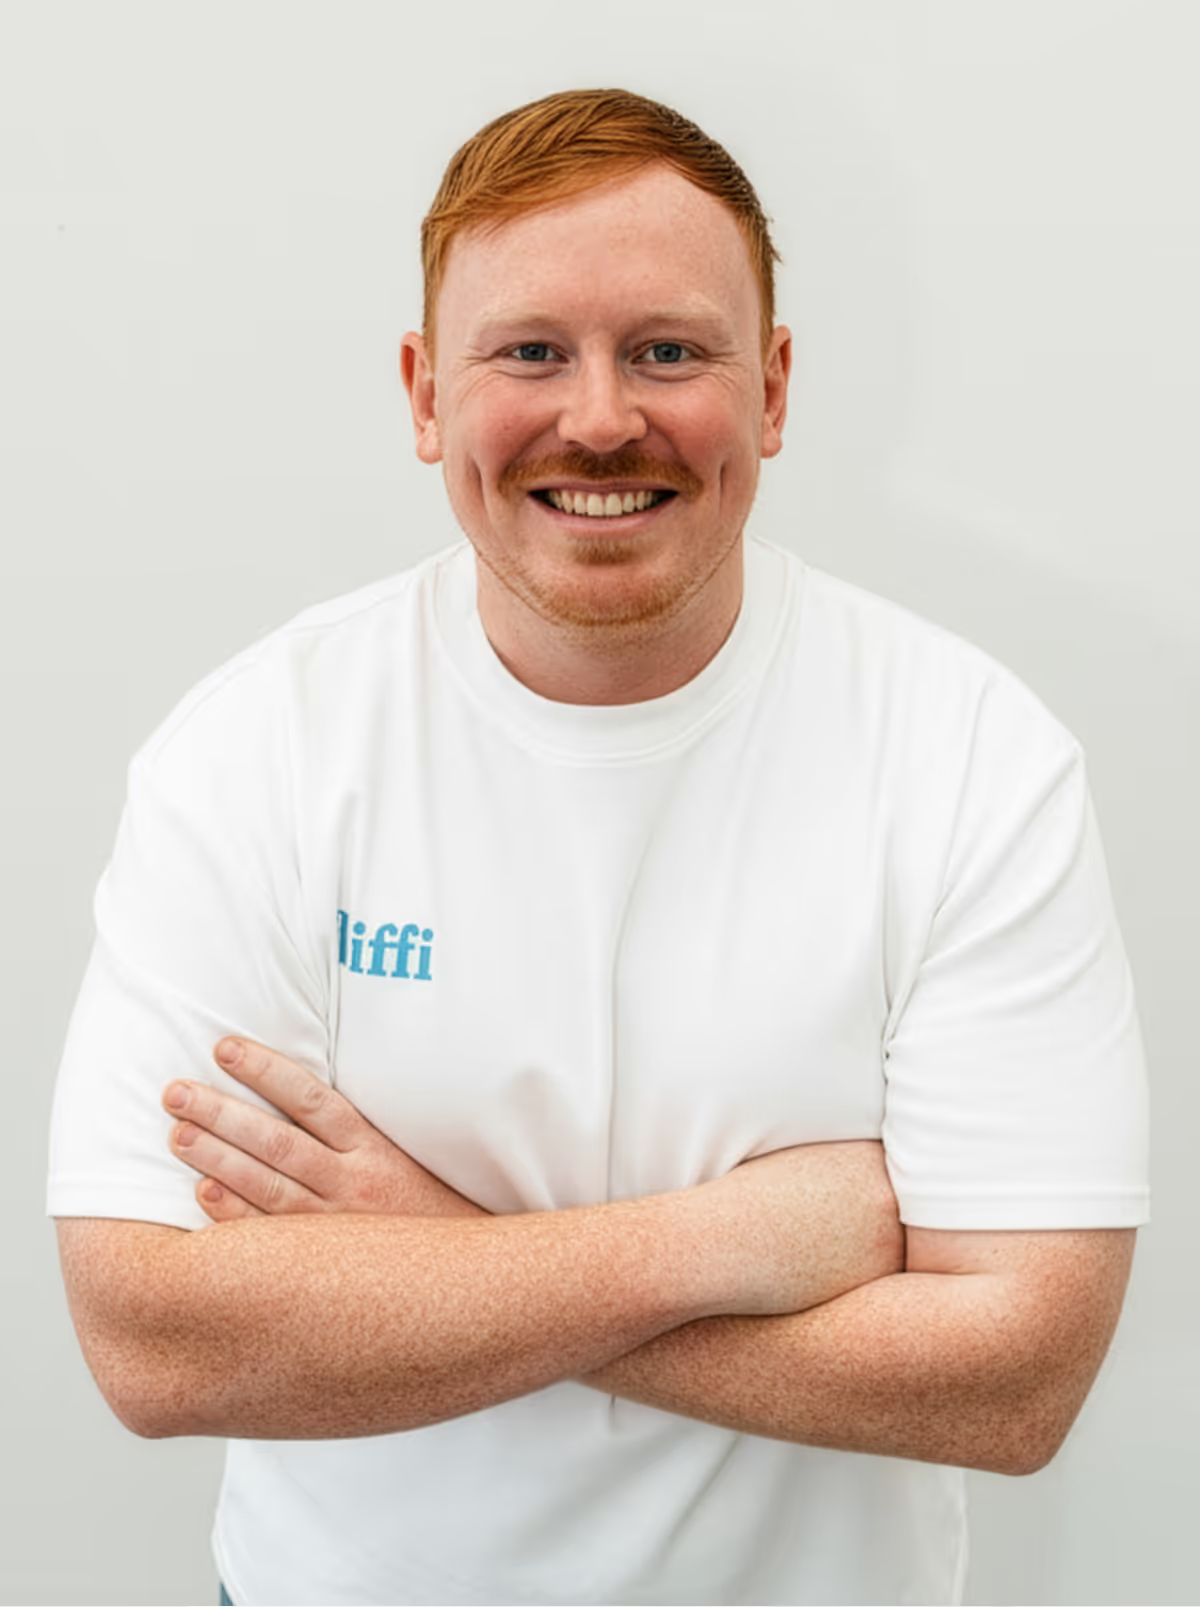
Jake Shelley
Managing Director and Co-founder
Jake has more than 15 years of experience scaling SaaS businesses. He was an early contributor at Deputy, starting as a junior developer and QA and rising to Senior Director of Global Delivery as it grew past $100M in annual revenue. He’s usually the first person you’ll talk to.
“This is a new world where a non-engineer can be the lead engineer. They don’t need someone to take it off them. They need someone to check it, set it up properly, and let them keep going.”
Vibe code audit FAQs
What is a vibe code audit?
What does the audit check?
What counts as a vibe-coded app?
Is it the same as an AI app security audit?
Do you rebuild my app?
How much does a vibe code audit cost?
A tool online checks it for $39. Why pay more?
How long does it take?
Can’t I just ask Claude to check it?
Can I keep building with AI after?
Will it be 100% secure after this?
What’s in Always-on Review?
Will I lose control of my app?
When is it not the right fit?
Before real data goes in, get it checked.

Send us a link and one sentence on what it does. We’ll reply within a working day.